Google Dismantles Massive Android Botnet Secretly Planted by Hardware Partner
Google has successfully neutralized a covert botnet operation that infected over one million media streaming devices through a backdoor installed by a hardware partner. The tech giant has severed all commercial relations with the offending Shenzhen-based manufacturer as cybersecurity investigations continue.
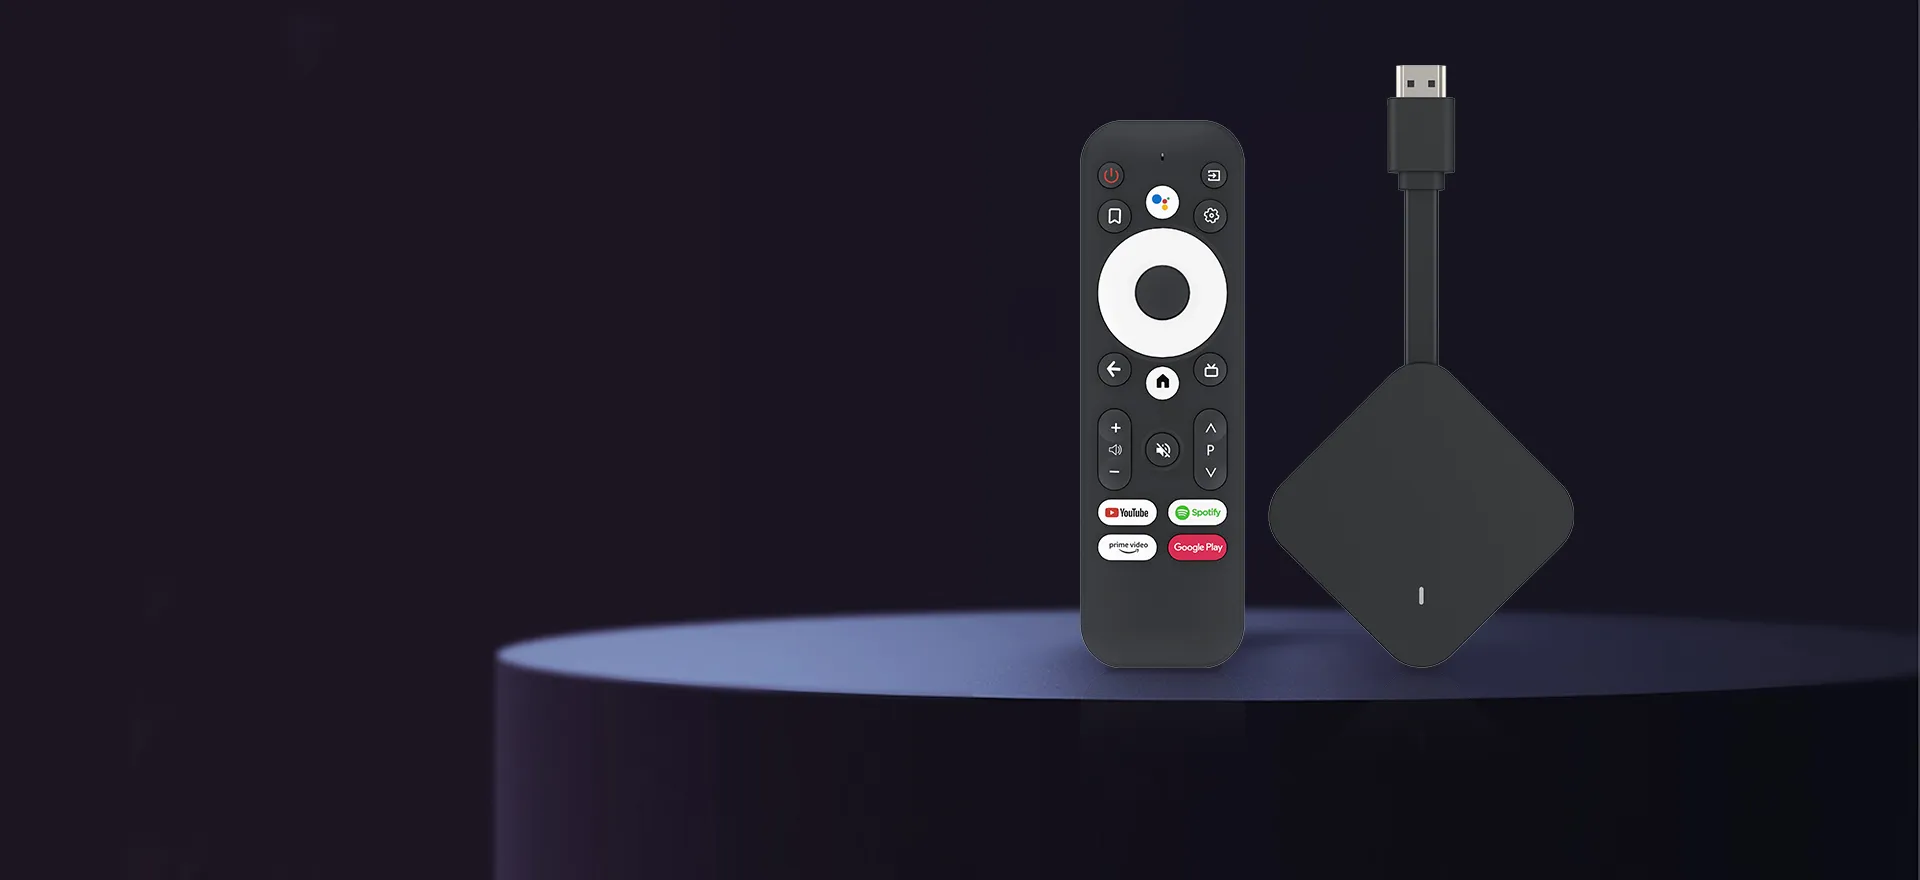
- An unnamed Android hardware manufacturer from Shenzhen, China, secretly embedded a malicious backdoor into approximately 1.3 million consumer set-top boxes.
- Google's security teams identified the threat, dismantled the infrastructure running the botnet, and immediately terminated its partnership with the vendor.
- The incident underscores severe vulnerabilities in the supply chain security of connected home entertainment hardware running open-source operating systems.
Google announced the successful neutralization of a sprawling botnet operation that commandeered roughly 1.3 million consumer set-top boxes, following the discovery that an unnamed hardware partner in Shenzhen, China, had secretly embedded a malicious backdoor into the firmware.
The breach highlights deep-seated vulnerabilities within the global hardware supply chain for Internet of Things (IoT) and connected living room devices. Historically, manufacturers operating white-label production lines have occasionally introduced unauthorized software layers, but utilizing over a million consumer units for clandestine botnet activities marks an unprecedented escalation in supply chain exploitation.
According to investigative reports initially highlighted by tech publication The Verge, Google's internal security divisions moved swiftly upon detecting the anomaly, executing targeted countermeasures to disable the rogue access points. Company representatives confirmed that commercial ties with the offending Shenzhen-based manufacturer have been permanently severed to protect the broader ecosystem.